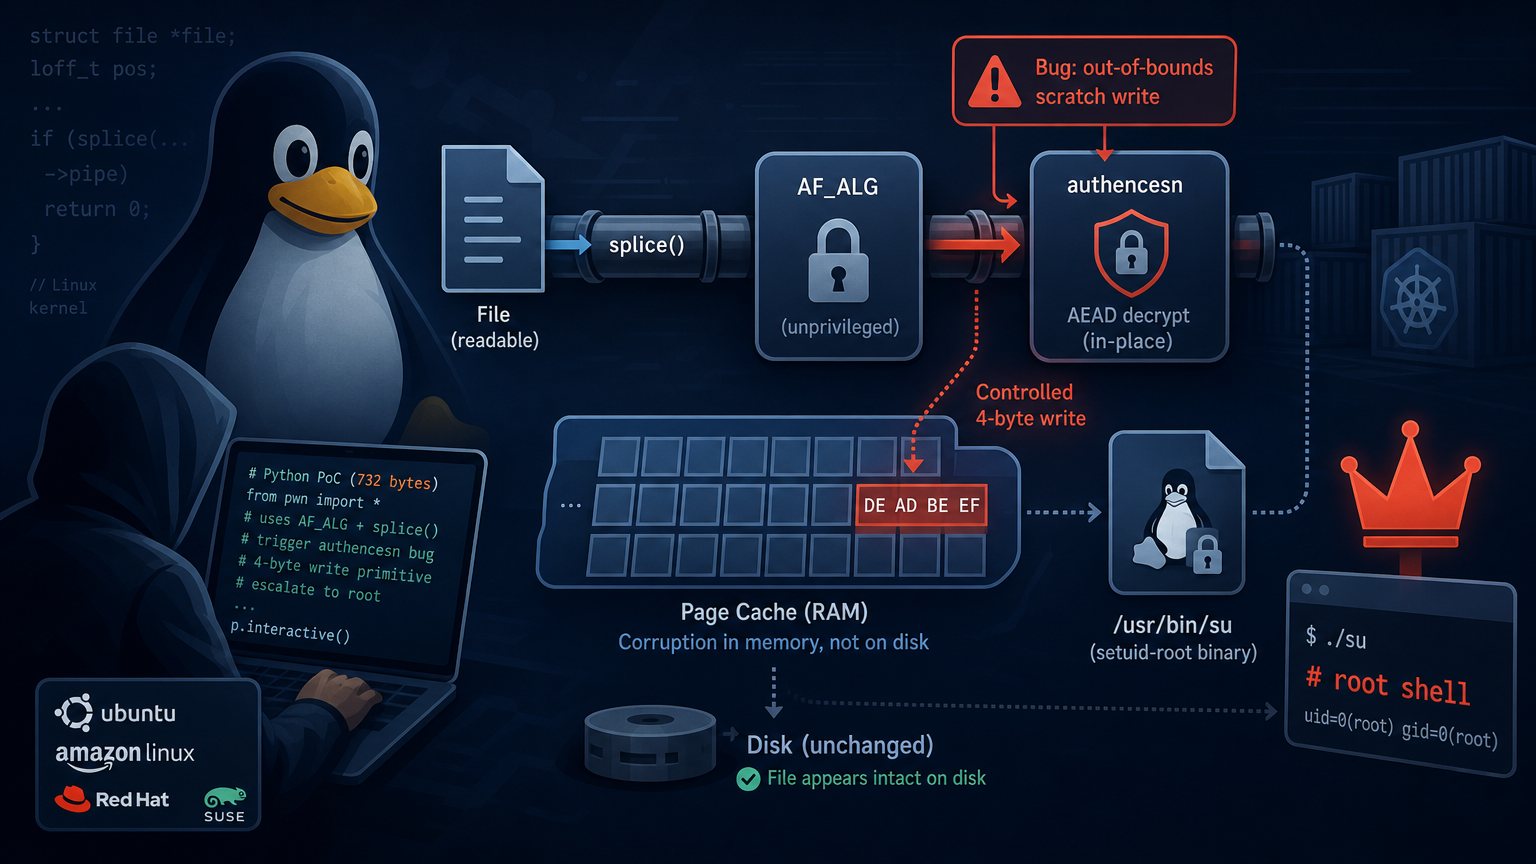
Copy Fail, tracked as CVE-2026-31431, is a newly disclosed Linux kernel vulnerability that can let a local user gain root privileges. According to Xint’s disclosure, it affects the kernel’s authencesn cryptographic template when used through AF_ALG and splice().
The bug allows a controlled 4-byte write into the page cache of any file the local user can read, without changing that file on disk. Xint says a 732-byte Python proof of concept gained root on tested Ubuntu, Amazon Linux, RHEL, and SUSE systems.
How cached data becomes executable code
The corruption changes the copy of a file held in memory. Its underlying contents on disk remain unchanged, so a file integrity check comparing checksums may still show it as clean. When Linux reads or executes the file, however, it may use the corrupted page-cache copy.
In Xint’s example, the exploit targets a setuid-root binary such as /usr/bin/su. A setuid-root program runs with root privileges. After the exploit alters its cached contents, executing the binary can run attacker-controlled code as root.
The vulnerable crypto operation
The flaw comes from an interaction between splice(), AF_ALG, and the kernel crypto subsystem. splice() can pass page-cache-backed file data into a pipe without copying it. AF_ALG makes kernel cryptographic operations available to unprivileged userspace programs.
In the vulnerable path, page-cache pages become part of a writable scatterlist, a structure that describes memory regions used by an operation. This happens during an in-place authenticated encryption with associated data (AEAD) decrypt operation. The authencesn implementation then makes a scratch write past the intended output boundary, placing attacker-controlled bytes in the cached file page.
Reliability, containers, and the fix
Xint describes Copy Fail as a straight-line logic flaw rather than a race condition. That means exploitation does not depend on the fragile timing required by some older kernel privilege-escalation bugs.
The disclosure also says the impact crosses container boundaries because the page cache is shared at the host level. That extends the concern beyond individual Linux servers to containerized and Kubernetes environments.
The fix reverts the vulnerable in-place AEAD behavior, separating the source and destination scatterlists so the operation no longer uses them in the vulnerable arrangement.


